Introduction
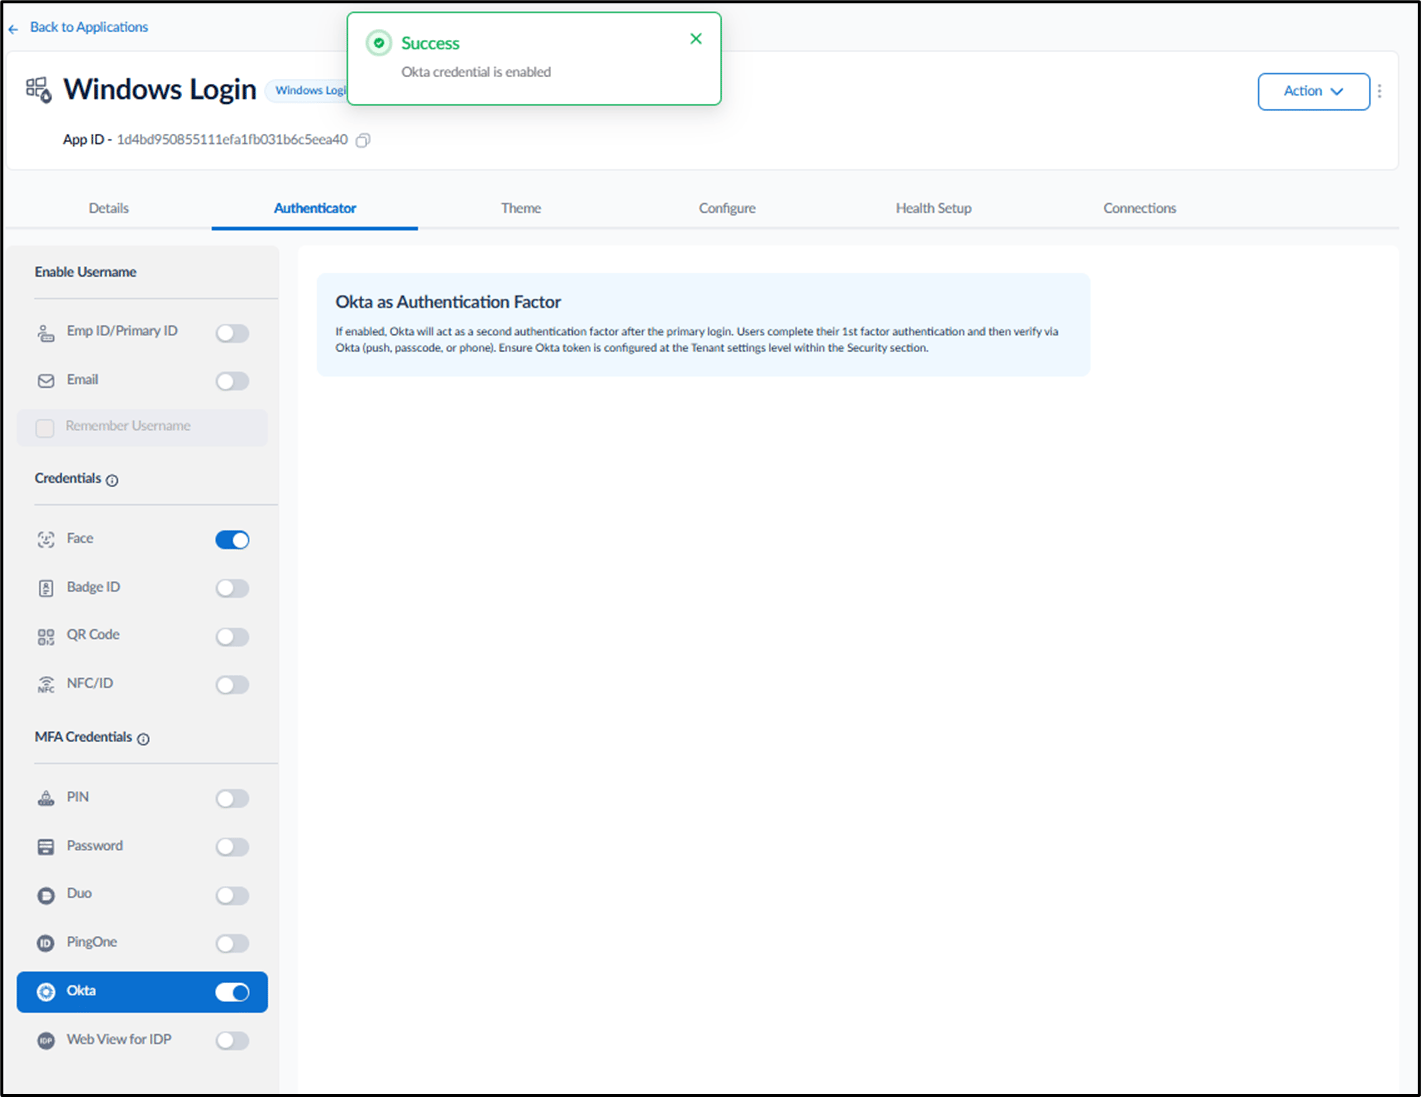
The OKTA feature in the Tenant Admin Portal allows admins to enable OKTA as a second factor authentication for the Windows Login application. When enabled with other primary factors, users can log in to endpoints using OKTA credentials as a second factor.Note: Windows Login supports Face, Badge, QR Code and NFC/ID as primary factor.
Prerequisite
You must have a Tenant Admin access in the Tenant Admin Portal.Steps to Enable OKTA MFA
- Log in to the Tenant Admin Portal.
- On the Applications page, select the Windows Login application.


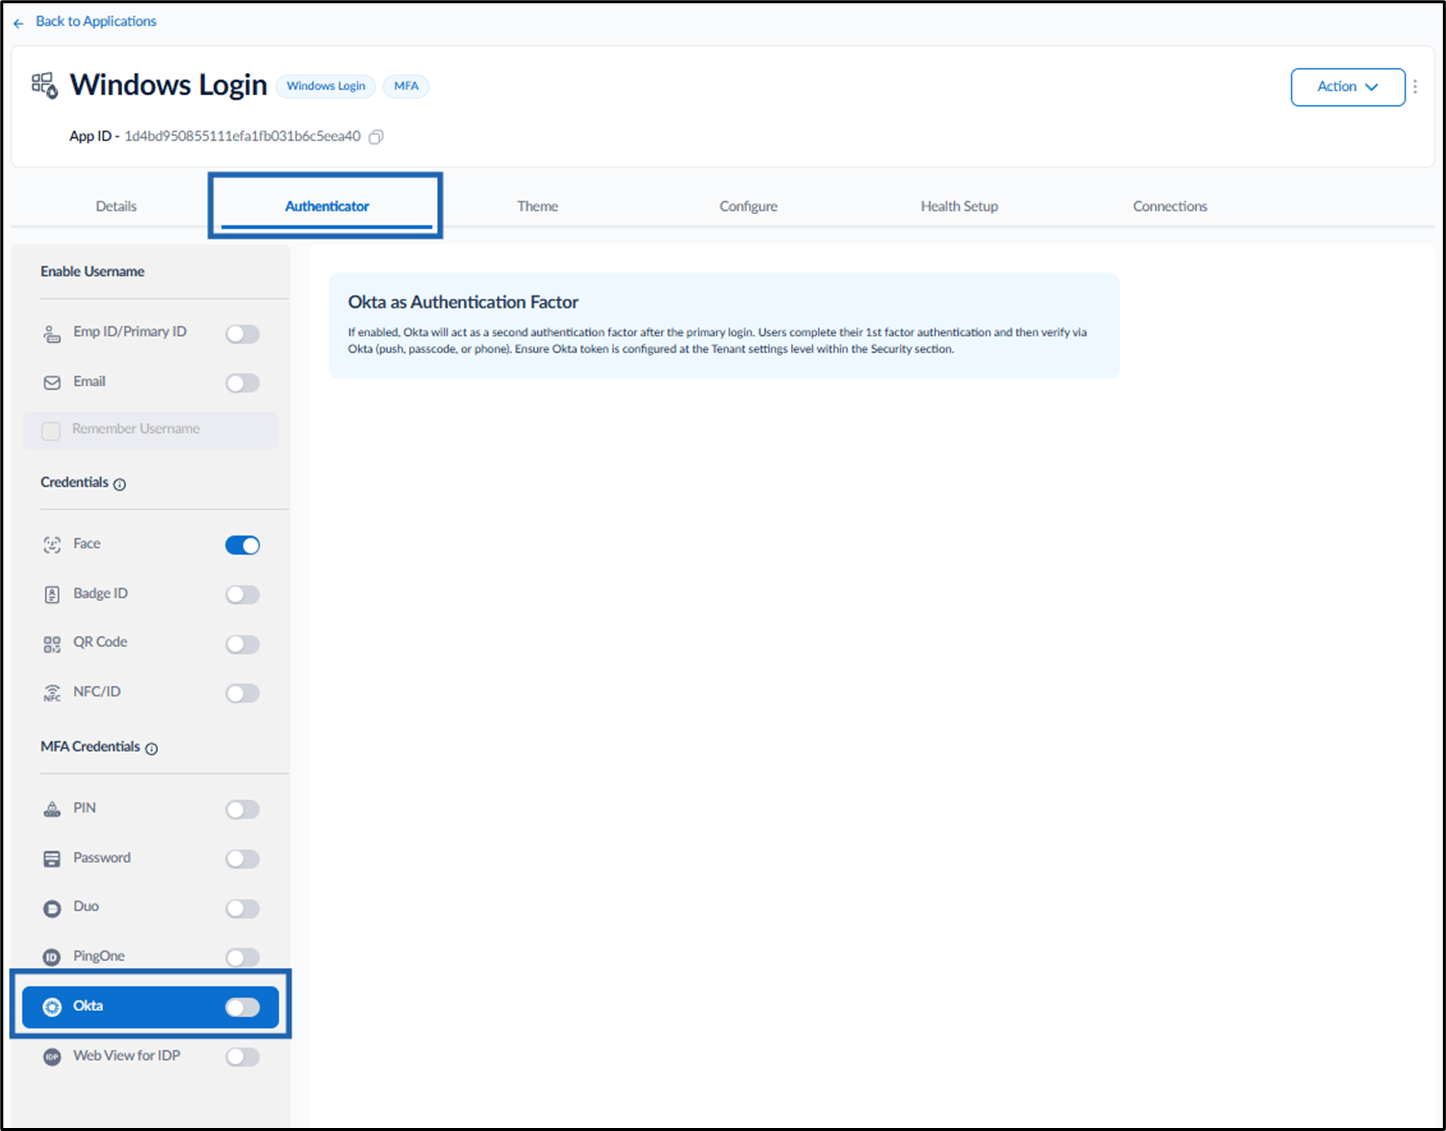
Note: You must do the Sync Configuration to apply changes.